Our clients trust us with some of their most sensitive information: emissions data, supplier records, portfolio company figures and numbers they have not yet published. Protecting that data is part of our job.
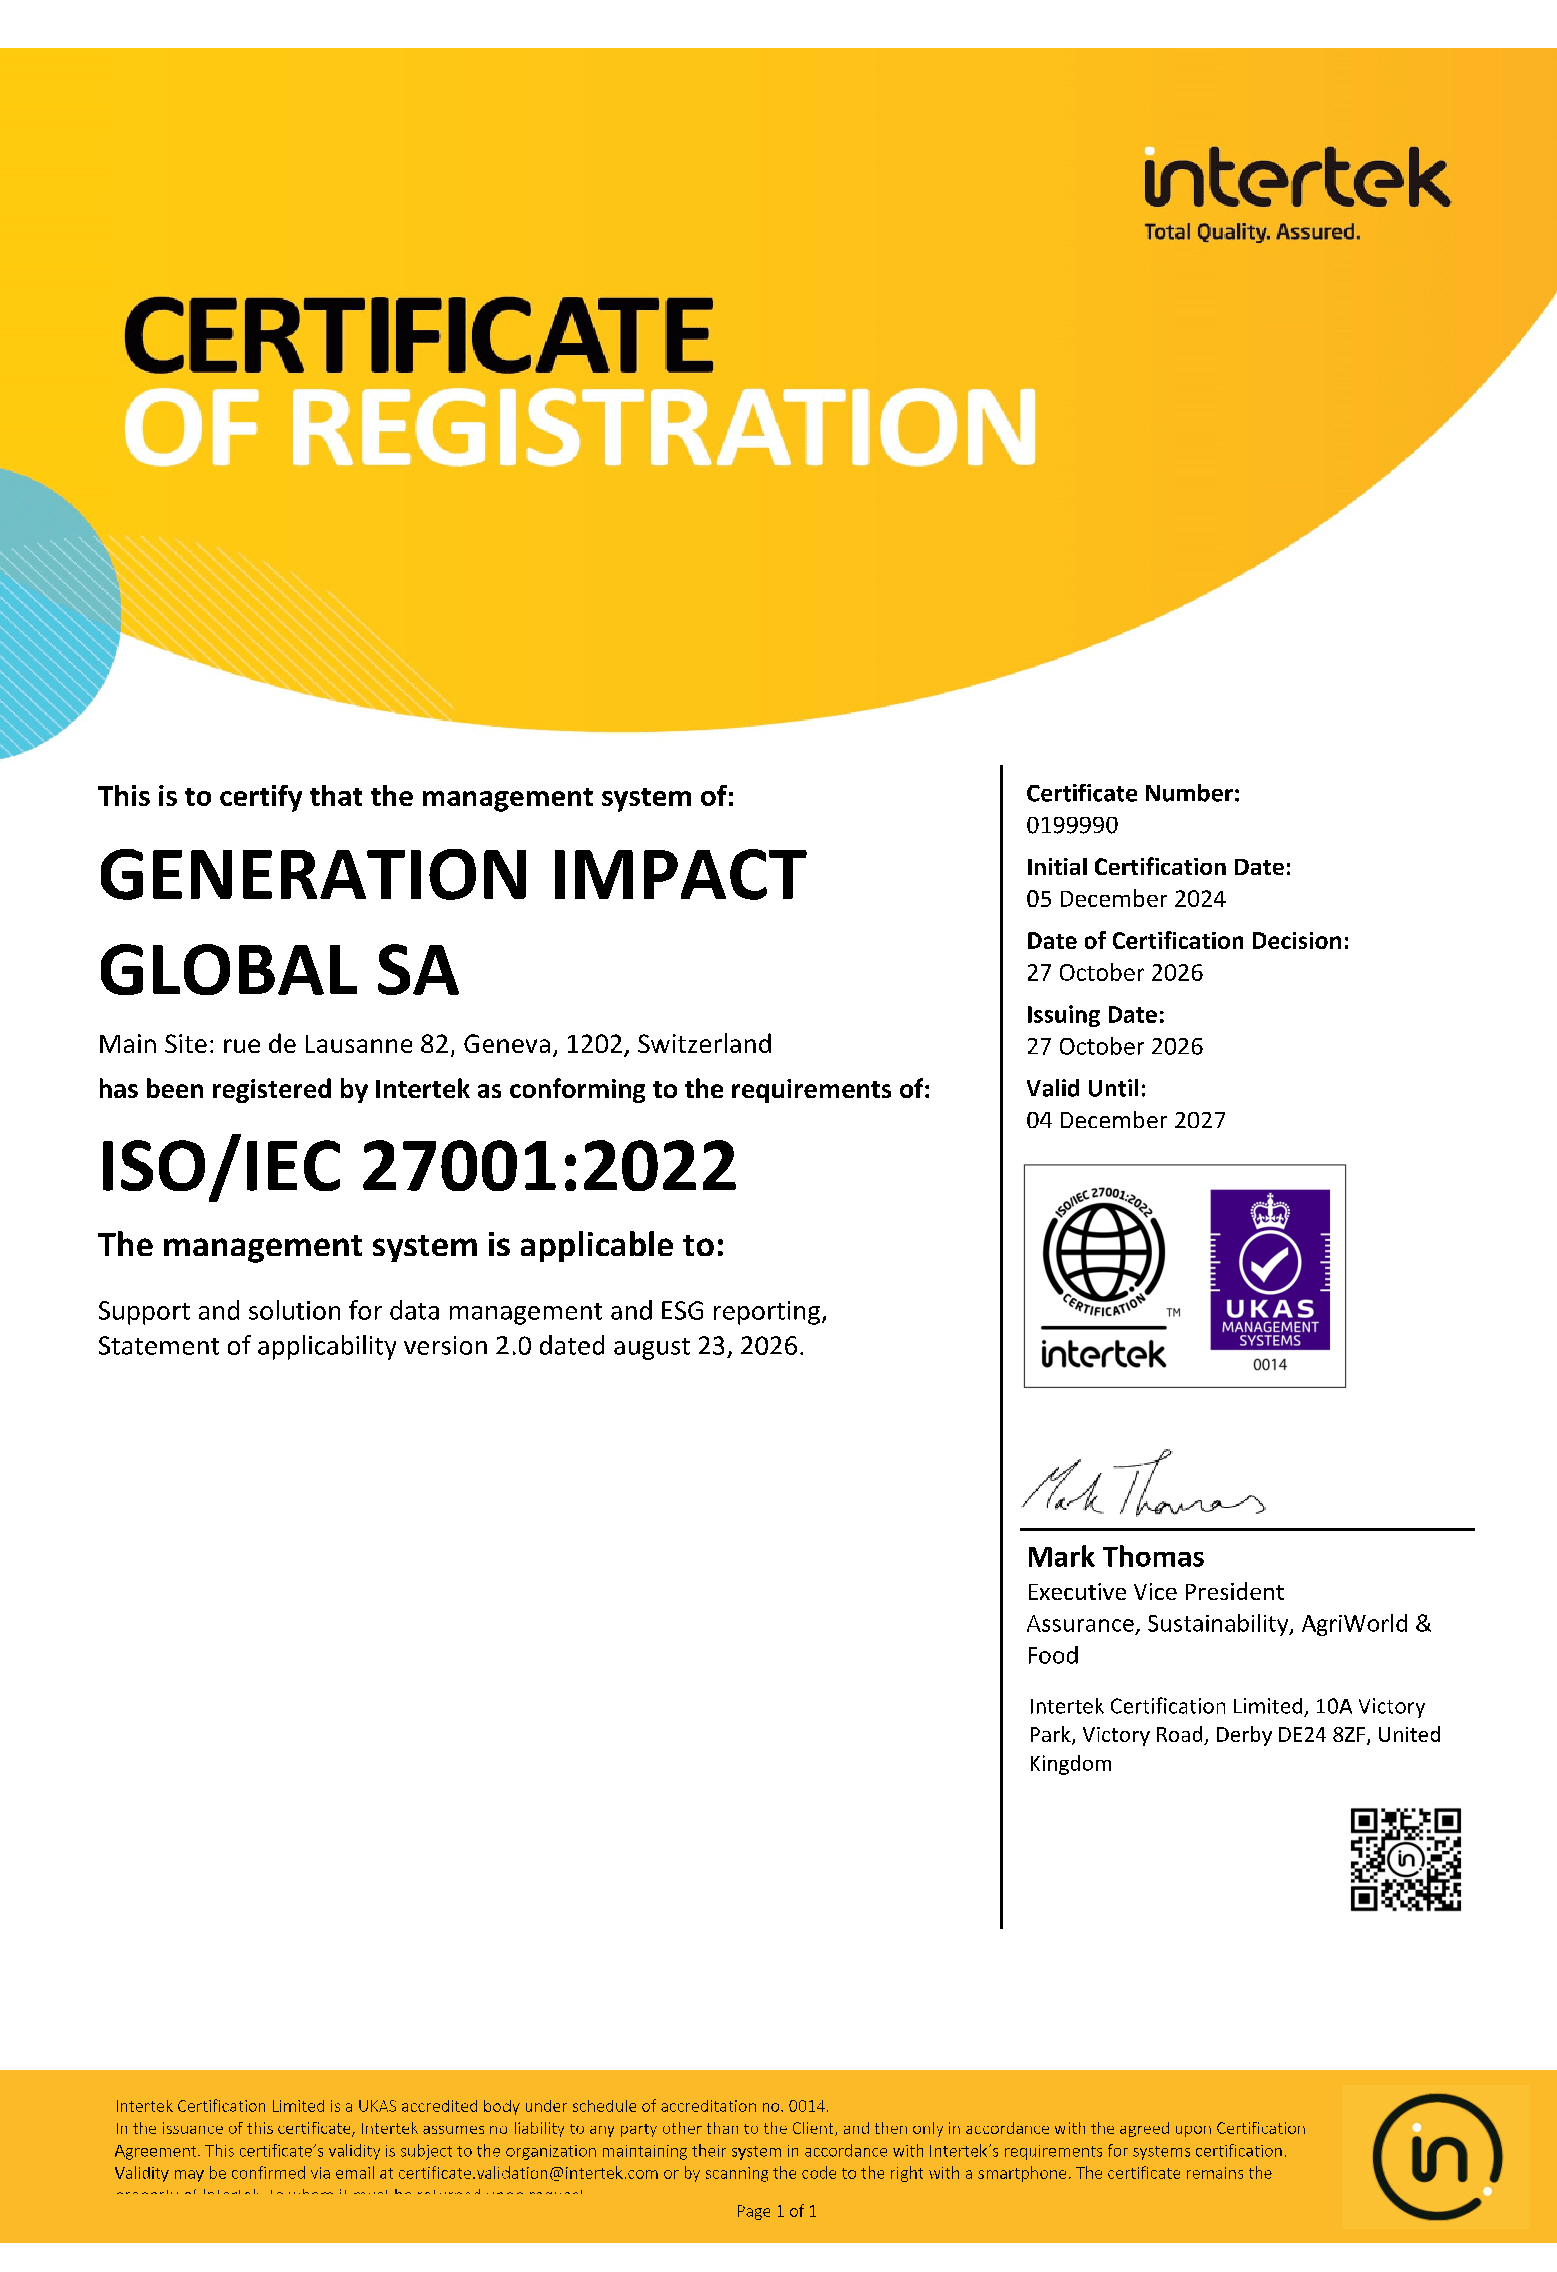
Generation Impact Global has kept its ISO/IEC 27001:2022 certification after our second surveillance audit with Intertek. Our certificate was reissued on 27 October 2026 and is valid until 4 December 2027.


“We built GIG to make ESG reporting easier for the companies and investors we work with. Easier should never mean less secure. Keeping our certification is how we show, every year, that we take care of the data our clients share with us.”
Anna Shpak
Founder & CEO, Generation Impact Global
Key facts
| Standard | ISO/IEC 27001:2022 |
| Certificate number | 0199990 (Intertek, UKAS accredited) |
| Valid until | 4 December 2027 |
| Scope | Support and solution for data management and ESG reporting |
What our clients keep on the GIG platform
We work with financial institutions, enterprises, SMEs and marketplaces across several countries. On our platform, they manage:
- SFDR data and principal adverse impact indicators
- CSRD reporting under ESRS, and EU Taxonomy alignment
- GRI reporting, as a GRI Licensed Software and Tools Partner
- greenhouse gas inventories and the activity data behind them
- ESG questionnaires sent to portfolio companies and suppliers
Much of this ends up in regulated disclosures. Companies in CSRD scope must have their sustainability statements checked by an assurance provider (limited assurance). Principal adverse impact data currently feeds SFDR disclosures. If this data were leaked, altered or lost, our clients would face regulatory and reputational risk as well as a technical problem.
Why it matters for our financial sector clients
Many of our clients are asset managers, funds and other financial institutions in the EU. Since 17 January 2025, the Digital Operational Resilience Act (DORA) has asked them to look closely at their software providers.
Under Article 28(5), financial entities may only contract ICT third-party service providers that comply with appropriate information security standards. For critical or important functions, they must also consider whether the provider uses the most up-to-date and highest quality standards.
DORA does not name a specific standard. In its Q&A DORA188-3200, EIOPA confirmed that the text refers to industry best practice. ISO/IEC 27001 is one of the most widely recognised ways for a provider to show it meets that expectation.
Our certificate does not replace a client’s own assessment. It makes that assessment faster and gives it independent evidence.
How we look after your data
We have held ISO/IEC 27001 certification since December 2024 and have passed two surveillance audits since, in September 2025 and October 2026.
In practice, this is how we work:
- Daily security testing. Automated scans and tests run every day, and we have kept the results since October 2024.
- Clear ownership. We keep a register of risks, assets and access rights, and review who can access what.
- Independent checks. An independent auditor from outside GIG carries out our internal audit each year, followed by a management review.
- Findings closed properly. Every finding goes through a formal corrective action process with an owner and a deadline.
- Cloud only. We are a fully remote team with no on-premise infrastructure, which keeps our environment simpler to control.
What this means for you
- Financial institutions: use our certificate in your ICT third-party due diligence and to support your register of information entries.
- Companies and SMEs: share it with your auditors, investors and procurement teams as part of your own supply chain checks.
- Security questionnaires: our team will help you complete them. Just ask us.
Frequently asked questions
Is GIG ISO 27001 certified?
Yes. Generation Impact Global holds ISO/IEC 27001:2022 certification (no. 0199990), issued by Intertek and valid until 4 December 2027. We have been certified since December 2024.
Does DORA require ISO 27001?
No. DORA asks financial entities to use ICT providers that follow appropriate information security standards, without naming one. ISO/IEC 27001 is one of the most widely accepted ways to show this.
What does GIG’s certificate cover?
The scope is our support and solution for data management and ESG reporting. This is the platform our clients use to collect, manage and report their ESG data.
Want to see how GIG keeps your ESG data secure and audit-ready?
We make it easy to do better.